
Is Bitcoin Safe From Quantum Computers?

Today, yes. No quantum computer that exists can break the cryptography protecting Bitcoin, and none is close. The threat is future and conditional, the quantum risks to Bitcoin fall on some chains and coins harder than others, and the softest target is the BTC you leave sitting on an exchange.
A large enough quantum computer could one day run Shor’s algorithm to recover a private key from an exposed public key, the signature math Bitcoin uses to authorize spending. Bitcoin’s mining and hashing rely on SHA-256, which a quantum computer weakens only modestly, so the network itself is not the weak point. Your exposure boils down to two things: whether your public key is already visible, and who holds your keys. On both counts, coins held in an exchange wallet are the most exposed, and this guide explains why and what lowers the risk.
Background: What Public Key Exposure Means for Bitcoin
Data reveals that 6.04 million Bitcoin (BTC), about 30.2% of circulating supply, sit in wallets with exposed public keys, and crypto exchanges hold a disproportionate share of that vulnerable stack. Binance alone has 85% of its labeled Bitcoin balances in exposed addresses, putting an estimated $34 billion at theoretical quantum risk. The findings reframe the quantum computing debate from a distant protocol problem into an immediate custody hygiene issue that exchanges can address today.
Blockchain and crypto analytics company Glassnode published on-chain analysis, mapping Bitcoin’s supply against a specific vulnerability metric, which is public key visibility. When a Bitcoin wallet signs a transaction, the public key used to verify that signature gets permanently recorded on the blockchain. If a custodian reuses that address, leaves change outputs sitting there, or keeps directing deposits to a wallet that should have been cycled out, the public key stays visible indefinitely.
This visibility is key in a quantum computing scenario. In theory, quantum computers could one day become powerful enough to derive a private key from a known public key. Nobody can do this today, as hardware doesn’t exist at the required scale. But Glassnode’s analysis measures where the damage would land if it eventually does.
How 6 Million BTC Became Vulnerable
Glassnode breaks the exposed supply into two categories. The first, and largest, is operational risk, which refers to 4.12 million BTC tied to poor wallet management. This can be anything from address reuse, to partial spends without proper key rotation, to dormant deposit addresses that keep receiving funds after their public keys have been broadcast, and anything in between.
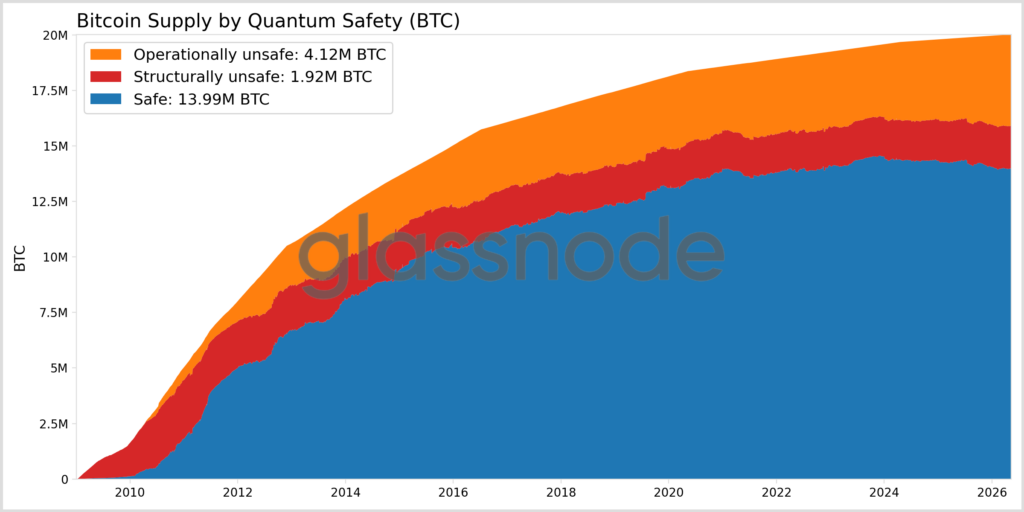
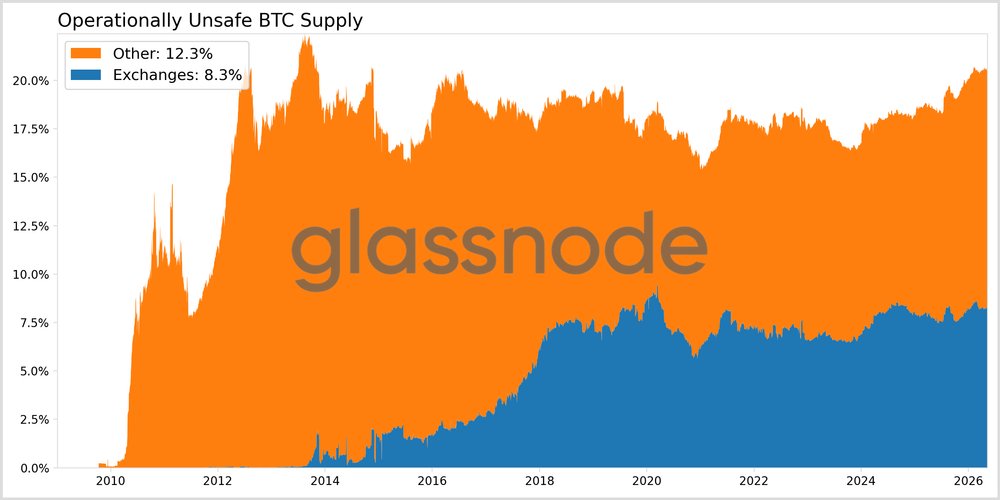
Exchanges account for around 1.66 million of those operationally exposed Bitcoin, which equals more than 8% of total issued supply. The proportion of exchange-held BTC classified as “operationally safe” has dropped from about 55% in 2018 to around 45% in 2026. That is a measurable decline in custody standards even as trading volumes and institutional participation have grown.
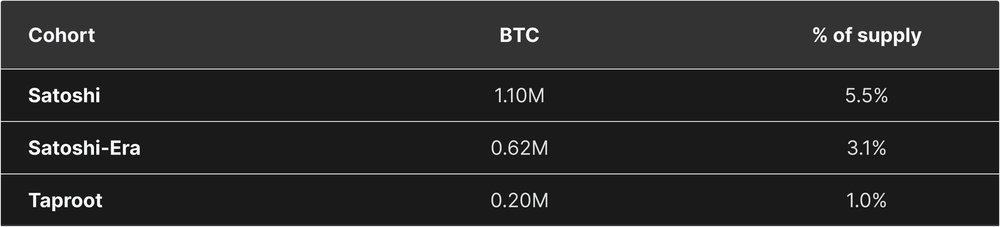
The second category is structural risk, which covers coins locked in legacy address formats or early-era wallets where the exposure is baked into the protocol layer. This portion is harder to fix and would require owner action or, in some cases, consensus-level changes to Bitcoin itself. Still, it accounts for the smaller share of the total exposed supply.
Exchange-by-Exchange Breakdown: The Custody Gap Is Enormous
The data splits crypto exchanges into clear tiers. Binance, the largest exchange by volume, carries 85% public key exposure across its labeled BTC wallets. With users holding over $40 billion in Bitcoin on the platform, that methodology places around $34 billion in the exposed group.
Bitfinex, Crypto.com, and Gemini each register 100% exposure on their labeled Bitcoin balances. Every single labeled wallet at these platforms has had its public key broadcast to the chain.
Coinbase sits at the other end with just 5% exposure. Whatever internal wallet rotation and address management policies Coinbase runs, they produce a dramatically different on-chain footprint. Coinbase also custodies a significant portion of Bitcoin ETF assets, which means its practices affect institutional holders who may never interact with the platform directly.
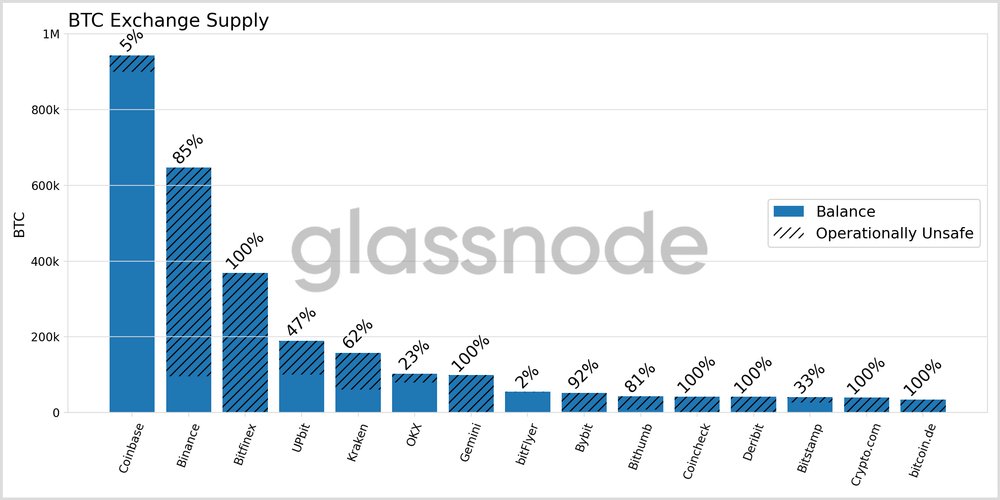
The disparity between Coinbase at 5% and Bitfinex at 100% says this is a policy and infrastructure problem and not really the result of an inherent limitation of holding large amounts of Bitcoin.
Wallets linked to the United States, United Kingdom, and El Salvador all maintain quantum safety rates above 99%. These are sovereign entities with their own operational complexity, seized asset management, and political considerations, yet their on-chain key hygiene is better than the majority of commercial crypto platforms.
This comparison completely deconstructs the argument that managing large BTC reserves inevitably creates exposure. It was the governments that figured out address rotation. Most exchanges haven’t, or at least they haven’t prioritized it.
Wall Street vs. Crypto-Native: The ETF Custody Question
The ETF landscape introduces another concern. Fidelity, which custodies its own spot Bitcoin ETF assets, shows around 2% exposure. This is institutional-grade key management applied to Bitcoin custody.
Grayscale, which converted its trust into an ETF structure, sits around 50%. WisdomTree registers close to 100%. These numbers deserve scrutiny for the sake of investors who bought Bitcoin ETFs assuming institutional custody standards would protect them. The ETF wrapper doesn’t automatically mean good wallet hygiene. The exposure is determined by the custodian’s internal practices.
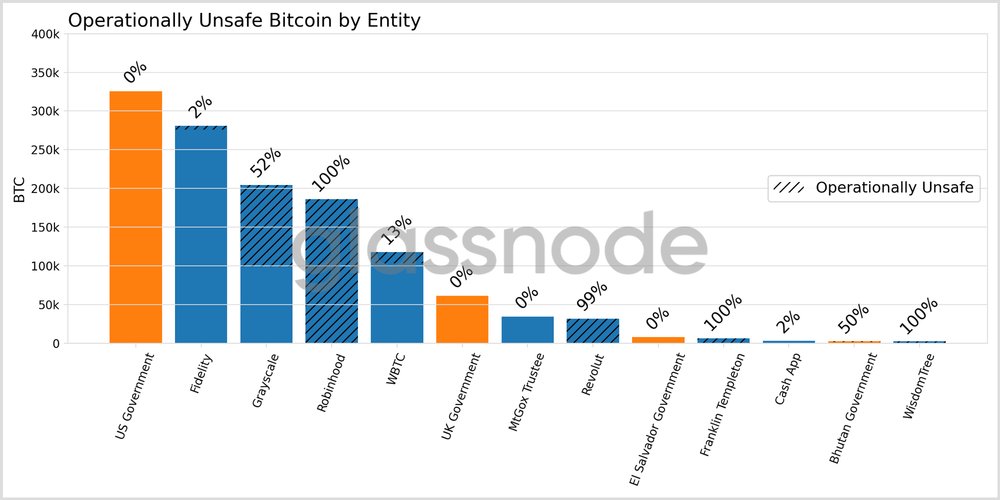
Retail platforms paint a similarly uneven picture. Block’s Cash App aligns with best practices, whereas Robinhood and Revolut show nearly complete public key exposure on their labeled wallets.
What Exchanges Can Do Right Now
The operational exposure identified by Glassnode is fixable even without any changes to Bitcoin’s protocol. Exchanges can move balances to fresh addresses with unexposed public keys and they can stop reusing deposit addresses. They can implement stricter change output management. None of this requires a fork of any kind or community consensus. It just needs a bit of internal engineering work and a decision to prioritize it.
Coinbase’s 5% number and the sub-1% government figures prove this is achievable at scale. The question is whether other exchanges will treat it as urgent.
A full migration to post-quantum cryptographic signatures across the Bitcoin network would need coordination among developers, miners, node operators, wallet providers, and custodians. Bitcoin’s consensus process moves slowly by design, so any systemic upgrade would unfold over years, and the community is yet to agree on which post-quantum signature scheme to adopt, let alone begin the implementation work.
This timeline gap is the core issue. The protocol fix is slow, but the custody fix is fast. Exchanges that wait for a protocol solution are leaving their users exposed to a risk they could reduce today.
Implications for Traders and the Broader Market
For traders, the Glassnode data introduces a new variable in platform risk assessment. Choosing where to hold Bitcoin is typically evaluated on factors like liquidity, fees, regulatory status, and insurance coverage. Public key exposure adds a measurable, on-chain dimension to that decision. A platform with 100% exposure and a platform with 5% exposure present different risk profiles, even if the quantum threat stays years away.
For the market in general, these findings place pressure on exchanges and custodians to publish their wallet hygiene metrics. As Bitcoin continues absorbing capital through ETFs and corporate treasury allocations, the entities holding the largest pools of customer coins will face increasing scrutiny over whether their custody infrastructure matches the security expectations of institutional and retail investors alike.
The Quantum Threat to Bitcoin: What Comes Next
The quantum computing threat to Bitcoin isn’t imminent, but the on-chain exposure to that threat is already here and concentrated in the places that hold the most customer funds. Glassnode’s data makes a clean case: roughly 30% of Bitcoin’s circulating supply has visible public keys, exchanges hold a disproportionate share of that exposure, and the fix for most of it is operational.
Exchanges that take wallet hygiene seriously will differentiate themselves as institutional adoption deepens. Those that don’t will eventually face uncomfortable questions from regulators and customers who can see the exposure data on-chain for themselves. The quantum clock may be uncertain, but the custody gap isn’t.
// FAQ
Will quantum computing break Bitcoin?
No, at least not with any quantum computer that exists today, and not for years. However, a future machine running Shor’s algorithm could derive a private key from an exposed public key. Therefore, the risk is genuine, but conditional on hardware nobody has built yet. Bitcoin’s SHA-256 mining is only modestly affected, so the weak point isn’t the network itself, but exposed signatures.
Can a quantum computer hack Bitcoin?
No quantum computer is close to the scale needed to recover a Bitcoin private key. If one is built, the coins most at risk are those whose public key is already visible on-chain, which makes reused and exchange-held addresses the easiest targets. Coins in unused addresses with no exposed public key are far better protected.
Is Bitcoin quantum-resistant?
Not by design: no Bitcoin address type is quantum-resistant today, though some expose far less than others. Which formats are safest, and how to hold coins in them, is covered in which Bitcoin addresses are quantum-vulnerable.
When could a quantum computer break Bitcoin?
No credible timeline puts it in the next few years. Estimates for a machine large and stable enough to run Shor’s algorithm against Bitcoin’s signatures range from about a decade to much longer, and they move with every hardware result. We compare the main predictions in our Q-Day timeline guide.
Which Bitcoin is most at risk from quantum computers?
Coins whose public key is already visible on-chain, which happens through address reuse, partial spends, and older address formats. Exchange-held balances concentrate that exposure, as the data above shows. Coins in a fresh address that has never signed a transaction are the best protected. You can check whether your own address has an exposed public key.
How do I protect my Bitcoin from quantum computers?
Use a new address for each transaction, move funds out of addresses with exposed public keys, and favor self-custody over leaving coins on an exchange. None of this needs a protocol change, and it closes most of the exposure today. See hot wallets vs cold wallets in a post-quantum world for the trade-offs.
How does Shor's algorithm affect Bitcoin?
Shor’s algorithm lets a large enough quantum computer recover a private key from an exposed public key, which is how it would forge a spending signature. It does not affect Bitcoin’s SHA-256 mining or rewrite confirmed blocks. Read our Shor’s algorithm guide.